Protected assets
Images, pods, workload identity
Images, pods, workload identity
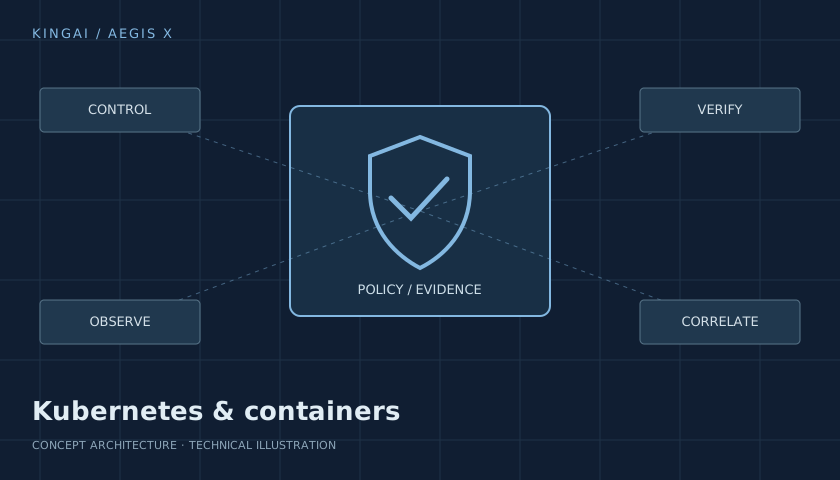
Images, pods, workload identity
SBOM, signatures, runtime controls
Asset inventory, access matrix, evidence-based risk register, simulation report and reversible response plan. Verify in a separately authorized environment before implementation.
Scenario signal and contextual review; no real system data.
SBOM, signatures, runtime controls
Verify scope, identity, expiry, rollback and service health before authorized action.
Record approval, compare service checks, retain rollback evidence.
Illustrative design and synthetic data only. No live connections, production claims, customer logos or real response actions.
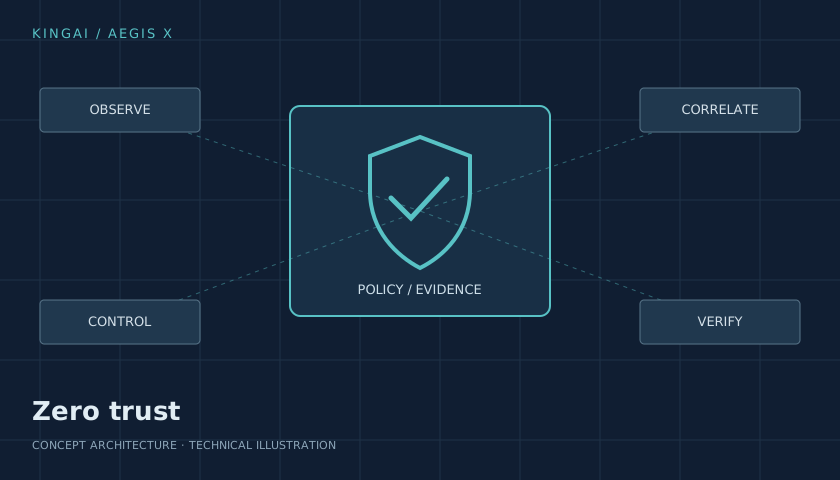
Verify every request with identity, device and resource context.
Explore solution →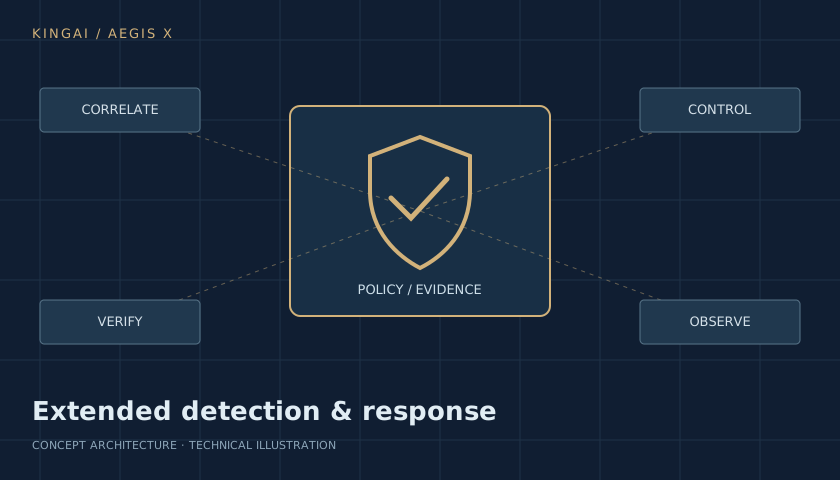
Correlate endpoint, identity and network events without interrupting critical services.
Explore solution →
Match authorized assets with public advisories and exploitation evidence.
Explore solution →
Detect unusual sessions and privilege changes.
Explore solution →